File validation - Signature sessions
You can validate the files chosen by the user during signature sessions using the mechanisms described in this article.
File naming rules
If you have a naming rule for the files you accept, you can configure your organization on Rest PKI Core to validate each file selected by the user with a regular expression that represents your rule. The rules are in the dashboard, under Settings, section Acceptable file name patterns.
Consider a hypothetical situation in which only files whose name starts with the letter P or X, followed by 6 digits and the .pdf
extension, are accepted. To enforce this condition, the naming rule would be configured as:
^[PX]\d{6}\.pdf$
The user would then be prevented from choosing files whose names do not match this pattern:
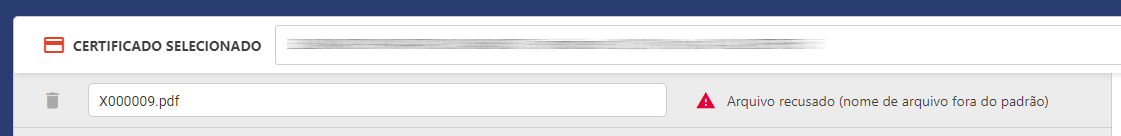
You can register several rules (Add new rule button). A file is accepted if its name matches any of them; if there are no rules, any name is accepted. Each rule has a File name pattern (the regular expression) and three options:
| Option | Effect |
|---|---|
| Match name only | The expression is matched against the name without its last extension: for P123456.pdf, against P123456. |
| Case sensitive | Without this option, matching ignores case: ^[PX]\d{6}\.pdf$ also accepts p123456.PDF. |
| Allow document key input | For files that match this rule, the user can enter the validation code the document should have (see below). |
The expression is not anchored automatically: it only has to be found somewhere in the name. Start it with ^ and end it with $ to require the
whole name to follow the pattern. For example, ph\d{9}\.pdf$ also accepts xyzph123456789.pdf, while ^ph\d{9}\.pdf$ does not.
The rules apply to the files the user chooses on the signature session page, that is, in sessions without predefined documents, and to the files signed with the command-line tool. Documents your application sends when creating the session are not checked.
Document key input
When the chosen file matches a rule with the Allow document key input option, the session page shows, below the file name, an Enter the document key field. There the user enters the validation code the signed document should have, instead of the system generating a new one, or ticks Auto-generate code. The file can only be signed after one of the two is filled in.
Rest PKI Core checks the code entered and refuses it if it doesn't follow the format of the organization's codes, doesn't exist or has already been used. The codes accepted are therefore the ones reserved beforehand by your application, as described in Allocating document validation keys, or by the allocate-keys command of the command-line tool.
Our developer support can help you write the regular expression from a textual description of your naming rule.
Maximum file size
The signature session page refuses files larger than the instance's upload limit, without uploading them or calling the validation API.
The limit is the General:MaxFileSize setting (default 100 MiB), which the server also enforces on uploads. On
on-premises instances, raise it if your users need to sign larger files.
File validation API
You can also configure a file validation API, implemented by your application, to be called to validate each file chosen by the user. Your application receives the file name (along with its MIME type and size in bytes) and returns whether the file should be accepted (and, if not, the reason for the rejection).
The validation request is an HTTP POST request whose payload is a ValidateFileRequest object (see the
API reference for the model definition). For example:
{
	"name": "P123456.pdf",
	"contentType": "application/pdf",
	"length": 2476032
}
Your application must respond with a ValidateFileResponse, as below:
{
	"accept": true,
	"rejectReason": null
}
Or, if the file is rejected:
{
	"accept": false,
	"rejectReason": "Message to the user"
}
The message returned by your application is shown to the user, for example: